> ## Documentation Index
> Fetch the complete documentation index at: https://docs.rodyne.xyz/llms.txt
> Use this file to discover all available pages before exploring further.
# Cnect identity linking
> Understand first-party Discord and Roblox ownership, conflicts, recovery, and unlinking.
Cnect is Rodyne's first-party identity surface. It confirms that a person controls the Discord and Roblox accounts used by community workflows.
## Link an identity
Members normally begin through `/verify`, `/link`, or a server's verification button. Cnect preserves the short-lived request through Discord sign-in and Roblox linking, then asks the member to confirm the exact accounts.
The resulting link can support:
* Mapped Discord role reconciliation.
* Staff-reviewed rank requests.
* Member Dash eligibility.
* Cross-community Cnect policy when separately configured.
## Conflicts
Rodyne stops rather than guessing when:
* Bloxlink and RoWifi return different Roblox IDs.
* A discovered Roblox account is already attached to another person's Cnect ownership.
* OAuth ownership changed.
* An active identity conflict is under review.
Imported or third-party member records do not create first-party ownership.
## Unlink and recovery
`/unlink` removes the member's Roblox OAuth connection and Cnect community links. It does not remove the Discord sign-in or automatically erase community records.
After unlinking:
* Cached and third-party discovery cannot silently restore the link.
* Old verification requests cannot restore it.
* The member can complete a fresh, explicit confirmation later.
* Account transfer to a different OAuth user does not transfer the previous person's historical releases.
## Privacy
Cnect's privacy page explains provider data, community and network sharing, required cookies, retention, unlinking, and request routes. Identity requests can be sent to **[hello@rodyne.xyz](mailto:hello@rodyne.xyz)**. Requests about a community's records should also go to that community's administrators.
A matching numeric ID from an import or provider lookup is not equivalent to current first-party ownership proof.
## Guided walkthrough
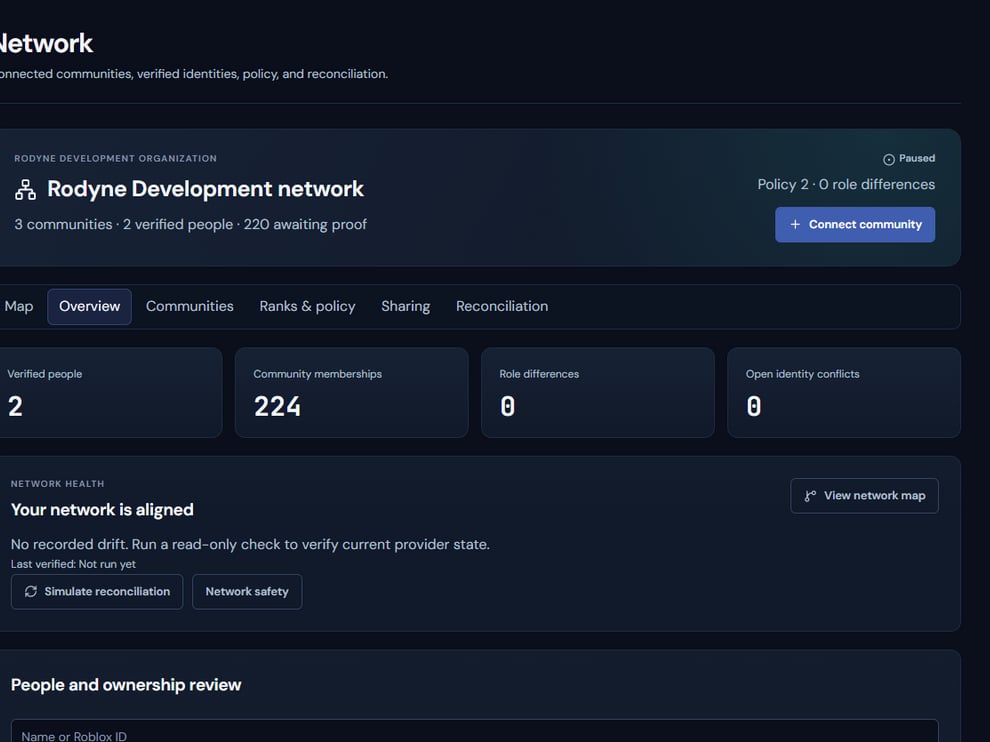 The screenshot above is from the live Rodyne product. Use it to orient yourself, but rely on the current record state and live provider checks when operating the workspace.
## Operating procedure
Use the member's verification entry point rather than importing ownership.
Complete Discord and Roblox provider proof in the same short-lived flow.
Confirm the exact account names and numeric IDs before linking.
Stop when an identity is already owned or third-party providers disagree.
Only after ownership is confirmed should role or network evaluation proceed.
## Acceptance checks
| Check | Ready when | If it is not ready |
| ---------- | ----------------------------------------------- | ---------------------------------- |
| Discord | Current guild member controls the session | Restart the Discord sign-in |
| Roblox | Current OAuth subject owns the selected account | Repeat provider proof |
| Uniqueness | No active conflicting owner exists | Use the supported conflict process |
## Failure recovery
Never resolve an ownership conflict by editing numeric IDs in a member record. Preserve both records, re-establish provider proof, and follow the audited recovery path.
## Continue the workflow